
Question 1
What is considered an "Identity Provider Initiated" login to an application?
Correct Answer:
A. After signing in to the CyberArk Identity portal, a user launches a SAML app by clicking an app tile.
What is considered an "Identity Provider Initiated" login to an application?
You are tasked to enforce certificate based authentication onto all the domain-joined Windows machines within your organization. Based on the inventory record, there are 1000 Windows machines, which include 150 standalone Windows machines. The enrollment will be conducted from either the office network or through the Virtual Private Network (VPN).
Which parameter(s) should you define within the enrollment code to ensure the security of the code and that only the authorized endpoints get registered?
On which operating systems can the CyberArk Authenticator desktop application be installed? (Choose two.)
Where can you download the CyberArk Identity mobile app? (Choose two.)
What is the most likely reason a CyberArk Identity admin would turn on the "Provisioning" feature within a Web App connector?
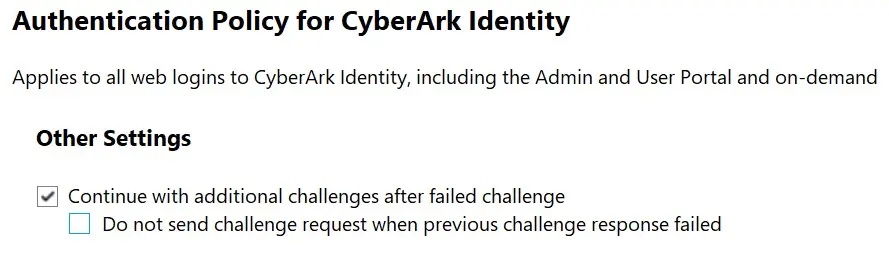
Refer to the exhibit.
Which statements are correct regarding this Authentication Policy? (Choose two.)
As part of compliance regulation, ACME Corporation is enforcing MFA for its critical business web-based application. To increase security and MFA compliance, CyberArk recommends selecting mechanisms from different categories. Within the authentication policy, ACME Corporation made the requirement to configure an authentication mechanism with "Something you know".
Which authentication mechanism meets this requirement?
A user's account information required for multi-factor authentication is not set up properly and is preventing the user from logging in.
What should you do?
CyberArk Identity has created a CLI integration with which vendor?
Your organization wants to limit access to the CyberArk Identity user portal to only corporate issued domain-joined laptops without the use of a VPN.
How can you achieve this?