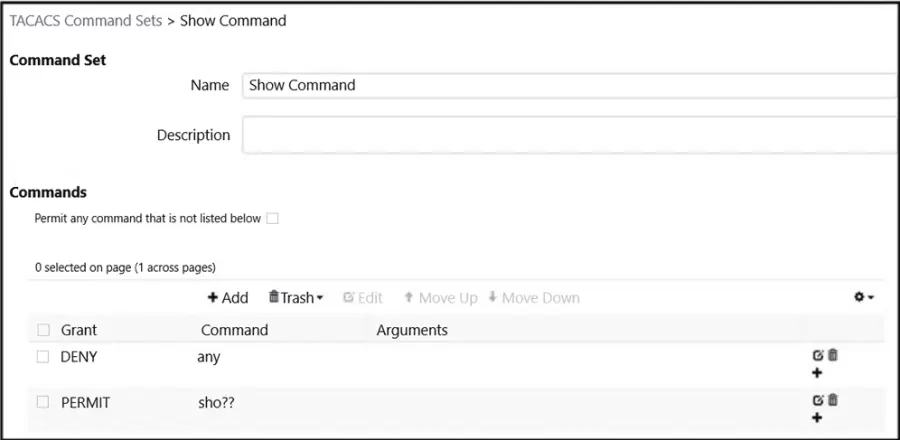
An engineer is creating a new TACACS* command set and cannot use any show commands after togging into the device with this command set authorization Which configuration is causing this issue?
Correct Answer:A. Question marks are not allowed as wildcards for command sets.
Question 2
MacOS users are complaining about having to read through wordy instructions when remediating their workstations to gam access to the network Which alternate method should be used to tell users how to remediate?
Which two methods should a sponsor select to create bulk guest accounts from the sponsor portal? (Choose two )
Correct Answer:A. Random; D. Imported
Question 4
What is a valid status of an endpoint attribute during the device registration process?
Correct Answer:B. pending
Question 5
Which portal is used to customize the settings for a user to log in and download the compliance module?
Correct Answer:C. Client Provisioning
Question 6
An engineer is enabling a newly configured wireless SSID for tablets and needs visibility into which other types of devices are connecting to it. What must be done on the Cisco WLC to provide this information to Cisco ISE9
IP Device Tracking (IPDT) is a feature that allows the Cisco WLC to track the IP addresses of devices that are connected to the wireless network. This information can then be provided to Cisco ISE, which can use it to identify the types of devices that are connecting to the network.
Question 7
The Cisco Wireless LAN Controller and guest portal must be set up in Cisco ISE. These configurations were performed:
* configured all the required Cisco Wireless LAN Controller configurations
* added the wireless controller to Cisco ISE network devices
* created an endpoint identity group
* configured credentials to be sent by email
* configured the SMTP server
* configured an authorization profile with redirection to the guest portal and redirected the access control list
* configured an authentication policy for MAB users
* created an authorization policy
Which two components would be required to complete the configuration? (Choose two.)
Correct Answer:C. sponsor portal; E. guest type
Question 8
An engineer deploys Cisco ISE and must configure Active Directory to then use information from Active Directory in an authorization policy. Which two components must be configured, in addition to Active Directory groups, to achieve this goat? (Choose two )
Correct Answer:A. Active Directory External Identity Sources; B. Library Condition for External Identity. External Groups
Question 9
A company manager is hosting a conference. Conference participants must connect to an open guest SSID and only use a preassigned code that they enter into the guest portal prior to gaining access to the network. How should the manager configure Cisco ISE to accomplish this goal?
Correct Answer:B. Create an access code to be entered in the AUP page.
Question 10
An engineer must deploy a WLAN that supports identity networking. The Cisco Wireless LAN Controller must be configured to apply the VLAN tag for client traffic returned by the RADIUS server. Which configuration parameter on the Cisco Wireless LAN Controller must be enabled to meet the requirement?
Correct Answer:C. Allow AAA Override
Explanation:
The Allow AAA Override setting must be enabled for the WLAN. AAA Override permits the Wireless LAN Controller to accept and apply authorization attributes returned by Cisco ISE through RADIUS, including the tunnel-type, tunnel-medium-type, and tunnel-private-group-ID attributes used for dynamic VLAN assignment. Without AAA Override, the controller generally retains the interface or VLAN statically configured on the WLAN and ignores the VLAN assignment returned by ISE. Change of Authorization allows ISE to modify or reauthenticate an existing session but does not itself enable dynamic VLAN assignment. A CWA redirect ACL is used for Central Web Authentication redirection. FlexConnect controls how access points switch client traffic at remote locations and is not the parameter that authorizes RADIUS-based VLAN overrides. The candidate file marks D, but that answer is technically incorrect; the verified answer is C.
Question 11
When configuring an authorization policy, an administrator cannot see specific Active Directory groups present in their domain to be used as a policy condition. However, other groups that are in the same domain are seen What is causing this issue?
Correct Answer:D. The groups are not added to Cisco ISE under the AD join point
A network engineer is configuring a network device that needs to filter traffic based on security group tags using a security policy on a routed into this task?
Correct Answer:B. cts cache enable
Question 13
Which file extension is required when deploying Cisco ISE using a ZTP configuration file in Microsoft Hyper-V?
Correct Answer:A. .iso
Question 14
What are the minimum requirements for deploying the Automatic Failover feature on Administration nodes in a distributed Cisco ISE deployment?
Correct Answer:D. a primary and secondary PAN and a health check node for the Primary PAN
Question 15
An engineer is designing a BYOD environment utilizing Cisco ISE for devices that do not support native supplicants Which portal must the security engineer configure to accomplish this task?