Limited-Time Offer: Enjoy 50% Savings! Ends in 00h 00m 00s Coupon code: 50OFF
Skip to content

Free Cisco Performing Cybersecurity Using Cisco Security Technologies 350-201 Exam Questions

Page: 1 / 14 Total 139 questions

Want more questions? Get Premium Access.

Question 1

An employee abused PowerShell commands and script interpreters, which lead to an indicator of compromise (IOC) trigger. The IOC event shows that a known malicious file has been executed, and there is an increased likelihood of a breach. Which indicator generated this IOC event?

Correct Answer: D. W32 AccesschkUtility.ioc
Question 2

An engineer received multiple reports from users trying to access a company website and instead of landing on the website, they are redirected to a malicious website that asks them to fill in sensitive personal dat

a. Which type of attack is occurring?

Correct Answer: D. Domain Name System poisoning

Question 3

An engineer notices that every Sunday night, there is a two-hour period with a large load of network activity. Upon further investigation, the engineer finds that the activity is from locations around the globe outside the organization's service are

a. What are the next steps the engineer must take?

Correct Answer: A. Assign the issue to the incident handling provider because no suspicious activity has been observed during business hours.

Question 4

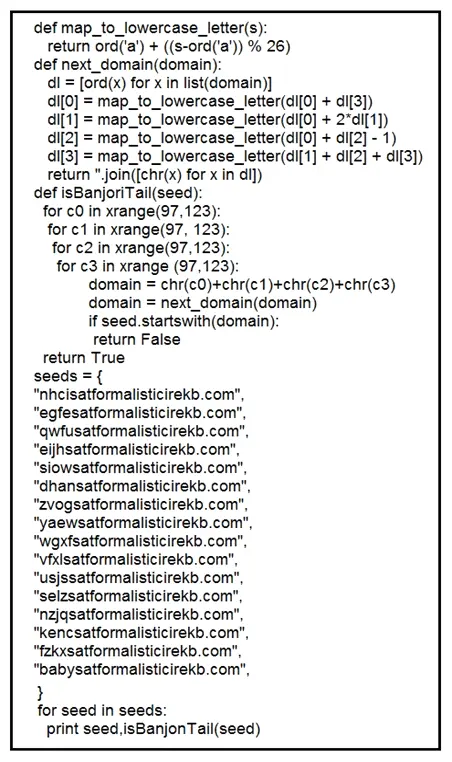
Refer to the exhibit.

What results from this script?

Correct Answer: B. A search is conducted for additional seeds

Question 5

A European-based advertisement company collects tracking information from partner websites and stores it on a local server to provide tailored ads. Which standard must the company follow to safeguard the resting data?

Correct Answer: D. GDPR

Question 6

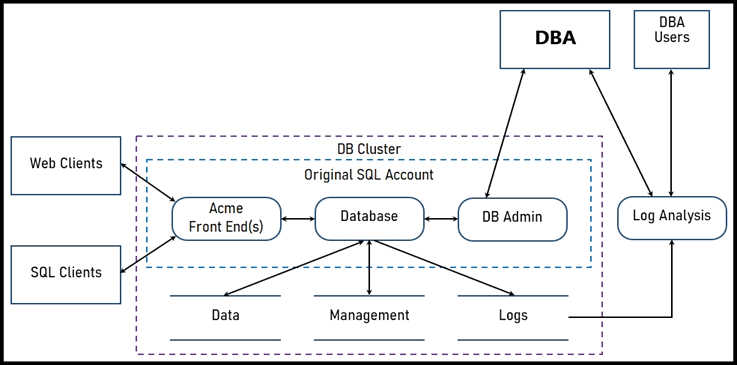
Refer to the exhibit.

Two types of clients are accessing the front ends and the core database that manages transactions, access control, and atomicity. What is the threat model for the SQL database?

Correct Answer: A. An attacker can initiate a DoS attack.

Question 7

An engineer receives an incident ticket with hundreds of intrusion alerts that require investigation. An analysis of the incident log shows that the alerts are from trusted IP addresses and internal devices. The final incident report stated that these alerts were false positives and that no intrusions were detected. What action should be taken to harden the network?

Correct Answer: C. Configure the proxy service on the IPS

Question 8

How does Wireshark decrypt TLS network traffic?

Correct Answer: A. with a key log file using per-session secrets

Question 9

A security analyst receives an escalation regarding an unidentified connection on the Accounting A1 server within a monitored zone. The analyst pulls the logs and discovers that a Powershell process and a WMI tool process were started on the server after the connection was established and that a PE format file was created in the system directory. What is the next step the analyst should take?

Correct Answer: C. Review the server backup and identify server content and data criticality to assess the intrusion risk

Question 10

An organization had an incident with the network availability during which devices unexpectedly malfunctioned. An engineer is investigating the incident and found that the memory pool buffer usage reached a peak before the malfunction. Which action should the engineer take to prevent this issue from reoccurring?

Correct Answer: D. Enable memory threshold notifications.