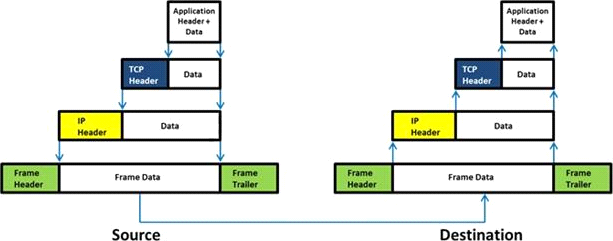
TCP/IP provides a broad range of communication protocols for the various applications on the network. The TCP/IP model has four layers with major protocols included within each layer. Which one of the following protocols is used to collect information from all the network devices?
Which of the following statement holds true for TCP Operation?
Correct Answer:D. Data transfer begins even before the connection is established
Question 3
The IP protocol was designed for use on a wide variety of transmission links. Although the maximum length of an IP datagram is 64K, most transmission links enforce a smaller maximum packet length limit, called a MTU.
The value of the MTU depends on the type of the transmission link. The design of IP accommodates MTU differences by allowing routers to fragment IP datagrams as necessary. The receiving station is responsible for reassembling the fragments back into the original full size IP datagram.
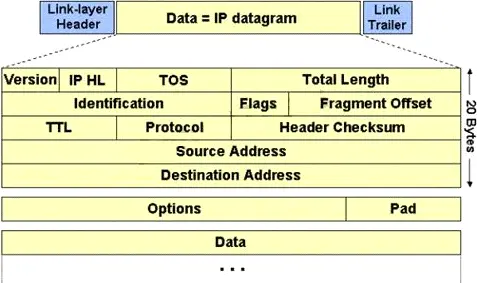
IP fragmentation involves breaking a datagram into a number of pieces that can be reassembled later. The IP source, destination, identification, total length, and fragment offset fields in the IP header, are used for IP fragmentation and reassembly.
The fragment offset is 13 bits and indicates where a fragment belongs in the original IP datagram. This value is a:
Correct Answer:C. Multiple of eight bytes
Question 4
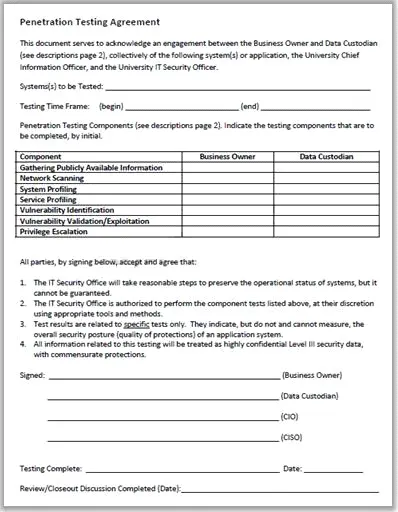
Why is a legal agreement important to have before launching a penetration test?
Correct Answer:C. It establishes the legality of the penetration test by documenting the scope of the project and the consent of the company.
Question 5
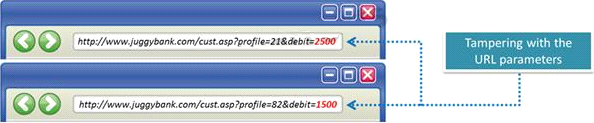
The Web parameter tampering attack is based on the manipulation of parameters exchanged between client and server in order to modify application data, such as user credentials and permissions, price and quantity of products, etc.
Usually, this information is stored in cookies, hidden form fields, or URL Query Strings, and is used to increase application functionality and control. This attack takes advantage of the fact that many programmers rely on hidden or fixed fields (such as a hidden tag in a form or a parameter in a URL) as the only security measure for certain operations.
Attackers can easily modify these parameters to bypass the security mechanisms that rely on them.
What is the best way to protect web applications from parameter tampering attacks?
Correct Answer:D. Applying effective input field filtering parameters
Question 6
What are the security risks of running a "repair" installation for Windows XP?
Correct Answer:D. Pressing Shift+F10 gives the user administrative rights
Question 7
Identify the type of testing that is carried out without giving any information to the employees or administrative head of the organization.
Correct Answer:B. Double Blind Testing
Question 8
Besides the policy implications of chat rooms, Internet Relay Chat (IRC) is frequented by attackers and used as a command and control mechanism. IRC normally uses which one of the following TCP ports?
Correct Answer:C. 6667 TCP port
Question 9
What does ICMP Type 3/Code 13 mean?
Correct Answer:D. Administratively Blocked
Question 10
Which of the following methods is used to perform server discovery?
Correct Answer:B. Who is Lookup
Question 11
The objective of social engineering pen testing is to test the strength of human factors in a security chain within the organization. It is often used to raise the level of security awareness among employees.
The tester should demonstrate extreme care and professionalism during a social engineering pen test as it might involve legal issues such as violation of privacy and may result in an embarrassing situation for the organization.
Which of the following methods of attempting social engineering is associated with bribing, handing out gifts, and becoming involved in a personal relationship to befriend someone inside the company?
Correct Answer:A. Accomplice social engineering technique
Question 12
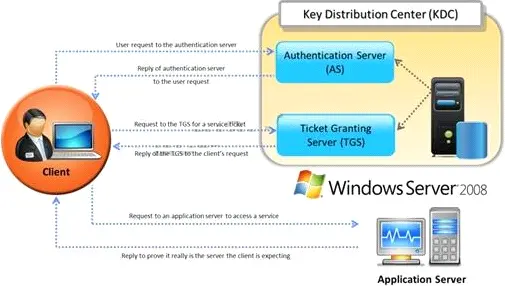
Identify the type of authentication mechanism represented below:
Correct Answer:D. Kerberos
Question 13
You work as a penetration tester for Hammond Security Consultants. You are currently working on a contractfor the state government of Californi
a. Your next step is to initiate a DoS attack on their network. Why wouldyou want to initiate a DoS attack on a system you are testing?
Correct Answer:C. List weak points on their network
Question 14
Which one of the following scans starts, but does not complete the TCP handshake sequence for each port selected, and it works well for direct scanning and often works well through firewalls?
Correct Answer:A. SYN Scan
Question 15
You have compromised a lower-level administrator account on an Active Directory network of a small company in Dallas, Texas. You discover Domain Controllers through enumeration. You connect to one of the Domain Controllers on port 389 using Idp.exe.
What are you trying to accomplish here?
Correct Answer:D. Enumerate domain user accounts and built-in groups