Limited-Time Offer: Enjoy 50% Savings! Ends in 00h 00m 00s Coupon code: 50OFF
Skip to content

Free GIAC Certified Enterprise Defender GCED Exam Questions

Page: 1 / 9 Total 88 questions

Want more questions? Get Premium Access.

Question 1

On which layer of the OSI Reference Model does the FWSnort utility function?

Correct Answer: C. Transport Layer
Explanation:

The FWSnort utility functions as a transport layer inline IPS.

Question 2

An analyst wants to see a grouping of images that may be contained in a pcap file. Which tool natively meets this need?

Correct Answer: A. Scapy

Question 3

To detect worms and viruses buried deep within a network packet payload, Gigabytes worth of traffic content entering and exiting a network must be checked with which of the following technologies?

Correct Answer: C. Packet matching

Question 4

The security team wants to detect connections that can compromise credentials by sending them in plaintext across the wire. Which of the following rules should they enable on their IDS sensor?

Correct Answer: C. alert tcp any 23 <> any 23 (msg:Telnet shell; class type:misc-attack;sid:100; rev:1;)

Question 5

When identifying malware, what is a key difference between a Worm and a Bot?

Correct Answer: D. A Bot gets instructions from an external control channel like an IRC server.

Question 6

You are responding to an incident involving a Windows server on your company's network. During the investigation you notice that the system downloaded and installed two files, iexplorer.exe and iexplorer.sys. Based on the behavior of the system you suspect that these files are part of a rootkit. If this is the case what is the likely purpose of the .sys file?

Correct Answer: C. It is a device driver used to load the rootkit

Question 7

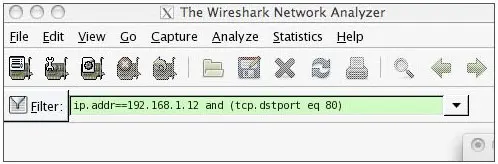
What information would the Wireshark filter in the screenshot list within the display window?

Correct Answer: B. Only traffic to or from IP address 192.168.1.12 and destined for port 80

Question 8

How does the Cisco IOS IP Source Guard feature help prevent spoofing attacks?

Correct Answer: A. Filters traffic based on IP address once a DHCP address has been assigned

Question 9

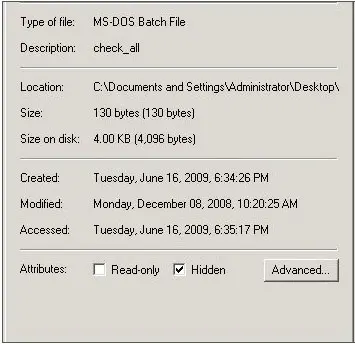
Which command tool can be used to change the read-only or hidden setting of the file in the screenshot?

Correct Answer: A. attrib
Explanation:

attrib --r or +r will remove or add the read only attribute from a file.


Question 10

Enabling port security prevents which of the following?

Correct Answer: C. Legitimate MAC addresses from being used to cause a Denial of Service condition