Free Google Professional Cloud Network Engineer Professional-Cloud-Network-Engineer Exam Questions
Page: 1 / 16Total 233 questions
Want more questions? Get Premium Access.
Question 1
You configured Cloud VPN with dynamic routing via Border Gateway Protocol (BGP). You added a custom route to advertise a network that is reachable over the VPN tunnel. However, the on-premises clients still cannot reach the network over the VPN tunnel. You need to examine the logs in Cloud Logging to confirm that the appropriate routers are being advertised over the VPN tunnel. Which filter should you use in Cloud Logging to examine the logs?
Correct Answer:C. resource.type= ''vpn_tunnel''
Question 2
Your organization is developing a landing zone architecture with the following requirements:
There should be no communication between production and non-production environments.
Communication between applications within an environment may be necessary.
Network administrators should centrally manage all network resources, including subnets, routes, and firewall rules.
Each application should be billed separately.
Developers of an application within a project should have the autonomy to create their compute resources.
Up to 1000 applications are expected per environment.
You need to create a design that accommodates these requirements. What should you do?
Correct Answer:C. Create a design that has one host project with a Shared VPC for the production environment, another host project with a Shared VPC for the non-production environment, and a service project that is associated with the corresponding host project for each initiative.
Explanation:
This design allows you to separate production and non-production environments while using Shared VPCs. Each environment has its own Shared VPC, and a service project is associated with each, allowing for separate billing and autonomy for developers. Centralized management of network resources is handled by the host projects.
Question 3
You are responsible for connectivity between AWS. Google Cloud, and an on-premises data center. Soon, the application team will deploy a data replication service that will move approximately 900 TB of data between Google Cloud and AWS daily. This data is sensitive and must be encrypted in transit. Your data center already has connections to both AWS and Google Cloud through 10 Gbps circuits. You need to configure additional connectivity between these environments and ensure the highest performance and lowest latency to meet business requirements. You also need to keep the existing connectivity topology to the on-premises data center the same. What should you do?
Correct Answer:A. (Q) * Deploy Cross-Cloud Interconnect connections between AWS and Google Cloud with 100 Gbps circuits.
* Create VLAN attachments in your VPC, configuring IPsec encryption on both sides of the connection.
* Use Cloud Router and BGP to exchange dynamic routes between AWS and Google Cloud.
Explanation:
The core requirement is to move a massive amount of sensitive data (900 TB daily) directly between Google Cloud and AWS with highest performance, lowest latency, and in-transit encryption, while maintaining existing on-premises connectivity.
Option A directly addresses this by recommending Cross-Cloud Interconnect with 100 Gbps circuits between AWS and Google Cloud. Cross-Cloud Interconnect is designed for high-throughput, low-latency connectivity between different cloud providers. The crucial part for sensitive data and encryption is 'configuring IPsec encryption on both sides of the connection,' as Cross-Cloud Interconnect itself provides a private path but not inherent encryption. Cloud Router and BGP are essential for dynamic route exchange. This option focuses on the direct cloud-to-cloud path for the high volume data transfer.
Options B and C involve upgrading the existing connections to the on-premises data center and routing all traffic through it. While this could work, it adds an unnecessary hop and likely higher latency for direct cloud-to-cloud traffic, making it less optimal for 'highest performance and lowest latency' between clouds. Additionally, removing existing 10Gbps circuits is not necessary and might impact the existing topology if not done carefully.
Option D suggests MACsec, which provides Layer 2 encryption. While good for physical security, for data replication services with sensitive data, IPsec (Layer 3 encryption) is more commonly used and flexible for end-to-end encryption across a routed network, and is typically preferred for data integrity and confidentiality over an IP network. Also, MACsec requires specific hardware support and is typically implemented at the interconnect termination points, not necessarily end-to-end for an application. Given the sensitive nature of the data and the large volume, IPsec provides the necessary transport-level encryption.
Exact Extract:
'Cross-Cloud Interconnect enables direct connectivity between your Google Cloud VPC networks and other cloud provider networks. It provides high-bandwidth, low-latency connections, ideal for large-scale data transfers between clouds.'
'For sensitive data, you can implement IPsec VPN tunnels over Cross-Cloud Interconnect connections to provide encryption in transit. This ensures data confidentiality and integrity over the dedicated interconnect.'
'Cloud Router dynamically exchanges routes between your Google Cloud VPC network and your other cloud network over the Cross-Cloud Interconnect connection using BGP.'Reference: Google Cloud Cross-Cloud Interconnect Documentation - Overview, Encryption options for hybrid connectivity
Question 4
You want to apply a new Cloud Armor policy to an application that is deployed in Google Kubernetes Engine (GKE). You want to find out which target to use for your Cloud Armor policy.
Which GKE resource should you use?
Correct Answer:D. GKE Ingress
Explanation:
Cloud Armour is applied at load balancers Configuring Google Cloud Armor through Ingress. https://cloud.google.com/kubernetes-engine/docs/how-to/ingress-features Security policy features Google Cloud Armor security policies have the following core features: You can optionally use the QUIC protocol with load balancers that use Google Cloud Armor. You can use Google Cloud Armor with external HTTP(S) load balancers that are in either Premium Tier or Standard Tier. You can use security policies with GKE and the default Ingress controller.
Question 5
You are configuring the final elements of a migration effort where resources have been moved from on-premises to Google Cloud. While reviewing the deployed architecture, you noticed that DNS resolution is failing when queries are being sent to the on-premises environment. You log in to a Compute Engine instance, try to resolve an on-premises hostname, and the query fails. DNS queries are not arriving at the on-premises DNS server. You need to use managed services to reconfigure Cloud DNS to resolve the DNS error. What should you do?
Correct Answer:A. Validate that the Compute Engine instances are using the Metadata Service IP address as their resolver. Configure an outbound forwarding zone for the on-premises domain pointing to the on-premises DNS server. Configure Cloud Router to advertise the Cloud DNS proxy range to the on-premises network.
Explanation:
To resolve DNS resolution issues for on-premises domains from Google Cloud, you should use Cloud DNS outbound forwarding zones. This setup forwards DNS requests for specific domains to on-premises DNS servers. Cloud Router is needed to advertise the range for the DNS proxy service back to the on-premises environment, ensuring that DNS queries from Compute Engine instances reach the on-premises DNS servers.
Question 6
Your team is developing an application that will be used by consumers all over the world. Currently, the application sits behind a global external application load balancer You need to protect the application from potential application-level attacks. What should you do?
Correct Answer:C. Create a Google Cloud Armor security policy with web application firewall rules, and apply the security policy to the backend service.
After a network change window one of your company's applications stops working. The application uses an on-premises database server that no longer receives any traffic from the application. The database server IP address is 10.2.1.25. You examine the change request, and the only change is that 3 additional VPC subnets were created. The new VPC subnets created are 10.1.0.0/16, 10.2.0.0/16, and 10.3.1.0/24/ The on-premises router is advertising 10.0.0.0/8.
What is the most likely cause of this problem?
Correct Answer:B. The more specific VPC subnet route is taking priority.
Question 8
You are adding steps to a working automation that uses a service account to authenticate. You need to drive the automation the ability to retrieve files from a Cloud Storage bucket. Your organization requires using the least privilege possible.
What should you do?
Correct Answer:C. Grant the read-only privilege to the service account for the Cloud Storage bucket.
Question 9
You recently deployed your application in Google Cloud. You need to verify your Google Cloud network configuration before deploying your on-premises workloads. You want to confirm that your Google Cloud network configuration allows traffic to flow from your cloud resources to your on- premises network. This validation should also analyze and diagnose potential failure points in your Google Cloud network configurations without sending any data plane test traffic. What should you do?
Correct Answer:C. Use Network Intelligence Center's Network Topology visualizations.
Question 10
You are designing a Partner Interconnect hybrid cloud connectivity solution with geo-redundancy across two metropolitan areas. You want to follow Google-recommended practices to set up the following region/metro pairs:
(region 1/metro 1)
(region 2/metro 2)
What should you do?
Correct Answer:B. Create a Cloud Router in region 1 with one VLAN attachment connected to metro1-zone1-x.
Create a Cloud Router in region 2 with two VLAN attachments connected to metro2-zone2-x.
Question 11
You are configuring a new application that will be exposed behind an external load balancer with both IPv4 and IPv6 addresses and support TCP pass-through on port 443. You will have backends in two regions: us-west1 and us-east1. You want to serve the content with the lowest possible latency while ensuring high availability and autoscaling. Which configuration should you use?
Correct Answer:D. Use Network Load Balancing in both regions, and use DNS-based load balancing to direct traffic to the closest region.
Question 12
You need to create a new VPC network that allows instances to have IP addresses in both the 10.1.1.0/24 network and the 172.16.45.0/24 network.
What should you do?
Correct Answer:C. Configure an alias-IP range of 172.16.45.0/24 on the virtual instances within the VPC subnet of 10.1.1.0/24.
Question 13
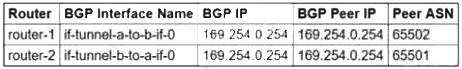
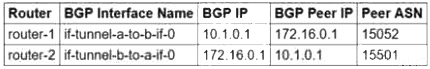
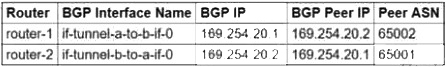
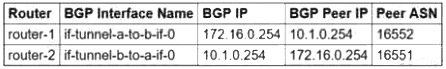
You need to configure the Border Gateway Protocol (BGP) session for a VPN tunnel you just created between two Google Cloud VPCs, 10.1.0.0/16 and 172.16.0.0/16. You have a Cloud Router (router-1) in the 10.1.0.0/16 network and a second Cloud Router (router-2) in the 172.16.0.0/16 network. Which configuration should you use for the BGP session?
A.
B.
C.
D.
Correct Answer:C. Option C
Question 14
You want to use Cloud Interconnect to connect your on-premises network to a GCP VPC. You cannot meet Google at one of its point-of-presence (POP) locations, and your on-premises router cannot run a Border Gateway Protocol (BGP) configuration.
Which connectivity model should you use?
Correct Answer:D. Partner Interconnect with a layer 3 partner
For Layer 3 connections, your service provider establishes a BGP session between your Cloud Routers and their edge routers for each VLAN attachment. You don't need to configure BGP on your on-premises router. Google and your service provider automatically set the correct configurations.
You have deployed a new internal application that provides HTTP and TFTP services to on-premises hosts. You want to be able to distribute traffic across multiple Compute Engine instances, but need to ensure that clients are sticky to a particular instance across both services.
Which session affinity should you choose?
Correct Answer:B. Client IP
Unlock Full
Professional-Cloud-Network-Engineer Exam Features