Limited-Time Offer: Enjoy 50% Savings! Ends in 00h 00m 00s Coupon code: 50OFF
Skip to content

Free HashiCorp Certified: Vault Associate (003) Exam HCVA0-003 Exam Questions

Page: 1 / 19 Total 285 questions

Want more questions? Get Premium Access.

Question 1

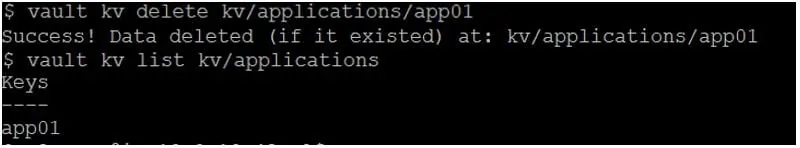
After issuing the command to delete a secret, you run a vault kv list command, but the path to the secret still seems to exist. What command would permanently delete the path from Vault?

Correct Answer: C. vault kv metadata delete kv/applications/app01
Explanation:

Comprehensive and Detailed in Depth Explanatio n:

A: Soft-deletes data, not metadata. Incorrect.

B: Destroys a version, not the path. Incorrect.

C: Deletes all metadata and versions, removing the path. Correct.

D: Invalid syntax. Incorrect.

Overall Explanation from Vault Docs:

''kv metadata delete deletes all versions and metadata for the key, permanently removing it.''


Question 2

You are using Azure Key Vault for the auto-unseal configuration on your cluster. After the Vault service restarts, what command must you run to unseal Vault?

Correct Answer: A. You don't need to run a command when using auto-unseal
Explanation:

Comprehensive and Detailed in Depth Explanatio n:

When using Azure Key Vault for auto-unseal, no manual command is required to unseal Vault after a service restart. The HashiCorp Vault documentation states: 'Vault supports opt-in automatic unsealing via cloud technologies: AliCloud KMS, AWS KMS, Azure Key Vault, Google Cloud KMS, and OCI KMS. This feature enables operators to delegate the unsealing process to trusted cloud providers to ease operations in the event of partial failure and to aid in the creation of new or ephemeral clusters.' Specifically, for Azure Key Vault, 'the auto-unseal feature automatically handles the unsealing process,' eliminating the need for manual intervention.

The documentation further explains: 'When configured with auto-unseal, Vault will automatically unseal itself upon startup using the configured key management service, provided the necessary permissions and credentials are in place.' Options like vault operator unseal are for manual unsealing, vault operator members lists cluster members, and vault operator init initializes Vault---none apply to auto-unseal scenarios. Thus, A is correct.


HashiCorp Vault Documentation - Auto Unseal with Azure Key Vault

HashiCorp Vault Documentation - Seal Concepts: Auto Unseal

Question 3

You are using Vault CLI and enable the database secrets engine on the default path of database/. However, the DevOps team wants to enable another database secrets engine for testing but receives an error stating the path is already in use. How can you enable a second database secrets engine using the CLI?

Correct Answer: C. vault secrets enable -path=database2 database
Explanation:

Comprehensive and Detailed In-Depth

Vault mounts secrets engines at unique paths, and only one engine can occupy a given path (e.g., database/). To enable a second database secrets engine, you must specify a different path using the -path flag: vault secrets enable -path=database2 database mounts a new instance at database2/. The type (database) defines the engine, and -path customizes its location, avoiding conflicts.

A: Incorrect syntax; lacks -path and misplaces database2/.

B: -force doesn't create a new path; it overwrites an existing engine, which isn't the goal.

D: Omits -path and engine type, making it invalid.

The secrets engine tutorial confirms -path is required for multiple instances of the same engine type.


Secrets Engines Tutorial

Secrets Enable Command

Question 4

How many Shamir's key shares are required to unseal a Vault instance?

Correct Answer: D. The threshold number of key shares
Explanation:

Shamir's Secret Sharing is a cryptographic algorithm that allows a secret to be split into multiple parts, called key shares, such that a certain number of key shares are required to reconstruct the secret. The number of key shares and the threshold number are configurable parameters that depend on the desired level of security and availability. Vault uses Shamir's Secret Sharing to protect its master key, which is used to encrypt and decrypt the data encryption key that secures the Vault data. When Vault is initialized, it generates a master key and splits it into a configured number of key shares, which are then distributed to trusted operators. To unseal Vault, the threshold number of key shares must be provided to reconstruct the master key and decrypt the data encryption key. This process ensures that no single operator can access the Vault data without the cooperation of other key holders. Reference: https://developer.hashicorp.com/vault/docs/concepts/seal4, https://developer.hashicorp.com/vault/docs/commands/operator/init5, https://developer.hashicorp.com/vault/docs/commands/operator/unseal6


Question 5

What is the difference between the TTL and the Max TTL (select two)?

Correct Answer: A. The TTL defines when the token will expire and be revoked; D. The Max TTL defines the maximum timeframe for which a token can be renewed
Explanation:

Comprehensive and Detailed in Depth Explanatio n:

Vault tokens have two key time attributes: TTL (Time-To-Live) and Max TTL (Maximum Time-To-Live), governing their lifecycle. Let's dissect each option:

Option A: The TTL defines when the token will expire and be revoked

The TTL is the current lifespan of a token before it expires. For example, a token with a TTL of 24h (vault token create -ttl=24h) expires 24 hours from creation unless renewed. Upon expiry, Vault revokes it automatically. This is a fundamental property of TTL, making this statement accurate. Correct.

Vault Docs Insight: ''The TTL defines when the token will expire... if it reaches its TTL, it will be revoked by Vault.'' (Core definition.)

Option B: The TTL defines when another token will be generated

TTL governs expiration, not token generation. New tokens are created explicitly (e.g., vault token create) or via auth methods, not automatically by TTL. This misunderstands TTL's role---it's about expiry, not regeneration. Incorrect.

Vault Docs Insight: ''TTL is the duration until expiration... New tokens are not generated by TTL.'' (No generation link.)

Option C: The Max TTL defines the timeframe for which a token cannot be used

This is backwards. Max TTL sets the upper limit a token can exist through renewals, not a period of inactivity or unusability. A token with a Max TTL of 72h can be renewed up to 72 hours from creation, after which it's revoked. This option inverts the concept. Incorrect.

Vault Docs Insight: ''Max TTL defines the maximum timeframe for which the token can be renewed... not a usage restriction.'' (Opposite meaning.)

Option D: The Max TTL defines the maximum timeframe for which a token can be renewed

Max TTL caps the total lifespan of a token, including renewals. For example, a token with TTL=24h and Max TTL=72h (vault token create -ttl=24h -explicit-max-ttl=72h) can be renewed twice (24h + 24h + 24h = 72h) before hitting the limit. Beyond 72h, renewal fails, and it expires. This is the precise definition of Max TTL. Correct.

Vault Docs Insight: ''The Max TTL defines the maximum timeframe for which the token can be renewed... Once reached, it cannot be renewed further.'' (Exact match.)

Detailed Mechanics:

TTL is dynamic, decreasing as time passes (e.g., vault token lookup shows ttl: 23h59m50s after 10 seconds). Renewal (vault token renew) resets TTL to its original value (e.g., 24h), but only up to Max TTL from creation. System defaults (768h/32 days) apply unless overridden. Periodic tokens (-period=24h) renew indefinitely within their period, ignoring Max TTL unless explicitly set.

Real-World Example:

Create: vault token create -ttl=1h -explicit-max-ttl=3h. After 1h, TTL=0, renewable. Renew at 2h total, TTL=1h again. At 3h total, Max TTL hits---revoked. Contrast with TTL-only: vault token create -ttl=1h, renewable up to system Max TTL (768h).

Overall Explanation from Vault Docs:

''The TTL defines when the token will expire... If it reaches its TTL, it will be immediately revoked by Vault. The Max TTL defines the maximum timeframe for which the token can be renewed... Once the Max TTL is reached, the token cannot be renewed any longer and will be revoked.'' These attributes ensure controlled token lifecycles.

Question 6

To secure your applications, your organization uses certificates generated by a public C

Correct Answer: B. PKI secrets engine
Explanation:

Comprehensive and Detailed In-Depth

The PKI secrets engine in Vault generates dynamic X.509 certificates, acting as a certificate authority (CA) or intermediate CA. It allows quick, cost-effective certificate creation for internal applications, with configurable TTLs and revocation capabilities, avoiding reliance on expensive public CAs. For example, vault write pki/issue/<role> generates a certificate instantly. The Identity engine (A) manages identities, not certificates. The SSH engine (C) handles SSH credentials, not X.509. The Transit engine (D) is for encryption, not certificate generation. The PKI docs highlight its suitability for this use case.


PKI Secrets Engine Docs

PKI Tutorial

Question 7

Your co-worker has asked you to perform certain operations in Vault and has provided you with a token accessor (not the token itself). What Vault operations would you be allowed to perform using only the provided accessor? (Select three)

Correct Answer: A. Renew the token to extend the TTL; B. Revoke the token in Vault to make it invalid; D. Lookup properties of the token, such as the TTL, policies, and metadata
Explanation:

Comprehensive and Detailed In-Depth

A token accessor is a reference to a token, not the token itself, and supports limited operations:

A: vault token renew -accessor extends the token's TTL if renewable, per the token docs.

B: vault token revoke -accessor revokes the token, making it invalid, a supported accessor action.

D: vault token lookup -accessor displays token properties (e.g., TTL, policies), a key accessor use case.

C: Creating child tokens requires the parent token, not just its accessor, as it involves authentication and policy inheritance, which accessors can't perform.

Accessors can't authenticate to Vault for secret access; they're for management tasks like these, per the tokens documentation.


Token Accessors

Token Commands

Question 8

Select the policies below that permit you to create a new entry of environment=prod at the path /secrets/apps/my_secret (select three).

Correct Answer: A. path 'secrets/+/my_secret' { capabilities = ['create'] allowed_parameters = { '*' = [] } }; C. path 'secrets/apps/my_secret' { capabilities = ['create'] allowed_parameters = { 'environment' = [] } }; D. path 'secrets/apps/*' { capabilities = ['create'] allowed_parameters = { 'environment' = ['dev', 'test', 'qa', 'prod'] } }
Explanation:

Comprehensive and Detailed in Depth Explanatio n:

This question requires identifying Vault policies that allow creating a new entry with environment=prod at the specific path /secrets/apps/my_secret. Vault policies define permissions using paths, capabilities, and parameter constraints. Let's evaluate each option:

Option A: path 'secrets/+/my_secret' { capabilities = ['create'] allowed_parameters = { '*' = [] } }

The + wildcard matches any single segment in the path, so this policy applies to /secrets/apps/my_secret. The create capability permits creating new entries at this path. The allowed_parameters = { '*' = [] } means any parameter (including environment) can be set to any value. This satisfies the requirement to create an entry with environment=prod. Thus, this policy is correct.

Option B: path 'secrets/apps/my_secret' { capabilities = ['update'] }

This policy targets the exact path /secrets/apps/my_secret but only grants the update capability. According to Vault's documentation, update allows modifying existing entries, not creating new ones. Since the question specifies creating a new entry, this policy does not meet the requirement and is incorrect.

Option C: path 'secrets/apps/my_secret' { capabilities = ['create'] allowed_parameters = { 'environment' = [] } }

This policy explicitly matches /secrets/apps/my_secret and grants the create capability, which allows new entries to be written. The allowed_parameters = { 'environment' = [] } specifies that the environment parameter can take any value (an empty list means no restriction on values). This permits setting environment=prod, making this policy correct.

Option D: path 'secrets/apps/*' { capabilities = ['create'] allowed_parameters = { 'environment' = ['dev', 'test', 'qa', 'prod'] } }

The * wildcard matches any path under secrets/apps/, including /secrets/apps/my_secret. The create capability allows new entries, and the allowed_parameters restricts environment to dev, test, qa, or prod. Since prod is an allowed value, this policy permits creating an entry with environment=prod and is correct.

Overall Explanation from Vault Docs:

Vault policies control access via paths and capabilities (create, read, update, delete, list). The create capability is required to write new data. Parameter constraints (allowed_parameters) further restrict what key-value pairs can be written. An empty list ([]) allows any value, while a populated list restricts values to those specified. A deny takes precedence over any allow, but no deny is present here.


Question 9

Which of the following are benefits of using the Vault Secrets Operator (VSO)? (Select three)

Correct Answer: A. Support for syncing from multiple secret sources; C. Automatic secret drift and remediation; D. Automatic secret rotation for multiple Kubernetes resource types
Explanation:

Comprehensive and Detailed in Depth Explanatio n:

The Vault Secrets Operator (VSO) enhances secrets management in Kubernetes. The HashiCorp Vault documentation lists its benefits: 'The following features are supported by the Vault Secrets Operator:

Support for syncing from multiple secret sources.

Automatic secret drift and remediation.

Automatic secret rotation for Deployment, ReplicaSet, StatefulSet Kubernetes resource types.'

The docs explain: 'VSO watches for changes to its supported Custom Resource Definitions (CRDs) and synchronizes secrets from Vault to Kubernetes Secrets, ensuring consistency (A). It detects and corrects unauthorized changes (C) and rotates secrets for specified resource types (D).' Bi-directional sync (B) is not supported---sync is one-way from Vault to Kubernetes. Thus, A, C, and D are correct.


HashiCorp Vault Documentation - Vault Secrets Operator

Question 10

Before the following command can be run to encrypt data, what (three) commands must be run to enable and configure the transit secrets engine in Vault? (Select three)

text

CollapseWrapCopy

$ vault write transit/encrypt/vendor \

plaintext="aGFzaGljb3JwIGNlcnRpZmllZA=="

Correct Answer: A. base64 <<< 'hashicorp certified'; D. vault secrets enable transit; E. vault write -f transit/keys/vendor
Explanation:

Comprehensive and Detailed in Depth Explanatio n:

To encrypt data using the Transit secrets engine, it must be enabled and configured. The HashiCorp Vault documentation states: 'Enable the Transit secrets engine at the default path of 'transit' using the command vault secrets enable transit. Create an encryption key called 'vendor' using the command vault write -f transit/keys/vendor. Encode the string using base-64 encoding by using the command base64 <<< 'hashicorp certified'.' These steps are prerequisites for the given vault write transit/encrypt/vendor command:

A (base64 <<< 'hashicorp certified'): The docs note, 'All plaintext data must be base64-encoded. The reason for this requirement is that Vault does not require that the plaintext is 'text'. It could be a binary file such as a PDF or image. The easiest safe transport mechanism for this data as part of a JSON payload is to base64-encode it.' The provided plaintext aGFzaGljb3JwIGNlcnRpZmllZA== is the base64 encoding of 'hashicorp certified.'

D (vault secrets enable transit): 'Before you can use the transit secrets engine, it must be enabled with vault secrets enable transit at the default path 'transit/'.'

E (vault write -f transit/keys/vendor): 'An encryption key must be created before encryption can occur. Use vault write -f transit/keys/vendor to generate a key named 'vendor'.'

B is the target command, not a prerequisite. C (vault secrets list) lists engines but doesn't configure Transit. Thus, A, D, and E are correct.


HashiCorp Vault Documentation - Transit Secrets Engine

Question 11

Which of the following statements are true about Vault policies? Choose two correct answers.

Correct Answer: C. Policies provide a declarative way to grant or forbid access to certain paths and operations in Vault; E. Policies deny by default (empty policy grants no permission)
Explanation:

Vault policies are written in HCL or JSON format and are attached to tokens or roles by name. Policies define the permissions and restrictions for accessing and performing operations on certain paths and secrets in Vault. Policies are deny by default, which means that an empty policy grants no permission in the system, and any request that is not explicitly allowed by a policy is implicitly denied1. Some of the features and benefits of Vault policies are:

Policies are path-based, which means that they match the request path to a set of rules that specify the allowed or denied capabilities, such as create, read, update, delete, list, sudo, etc2.

Policies are additive, which means that if a token or a role has multiple policies attached, the effective policy is the union of all the individual policies. The most permissive capability is granted if there is a conflict3.

Policies can use glob patterns, such as * and +, to match multiple paths or segments with a single rule. For example, path ''secret/*'' matches any path starting with secret/, and path ''secret/+/config'' matches any path with two segments after secret/ and ending with config4.

Policies can use templating to interpolate certain values into the rules, such as identity information, time, randomness, etc. For example, path ''secret/{{identity.entity.id}}/*'' matches any path starting with secret/ followed by the entity ID of the requester5.

Policies can be managed by using the vault policy commands or the sys/policy API endpoints. You can write, read, list, and delete policies by using these interfaces6.

The default policy is a built-in policy that is attached to all tokens by default and cannot be deleted. However, the default policy can be modified by using the vault policy write command or the sys/policy API endpoint. The default policy provides common permissions for tokens, such as renewing themselves, looking up their own information, creating and managing response-wrapping tokens, etc7.

You do not have to use YAML to define policies, as Vault supports both HCL and JSON formats. HCL is a human-friendly configuration language that is also JSON compatible, which means that JSON can be used as a valid input for policies as well8.

Vault does not need to be restarted in order for a policy change to take effect, as policies are stored and evaluated in memory. Any change to a policy is immediately reflected in the system, and any token or role that has that policy attached will be affected by the change.


Question 12

When generating a dynamic secret, what value is returned that a user can use to renew or revoke the lease?

Correct Answer: D. lease_id
Explanation:

Comprehensive and Detailed in Depth Explanatio n:

When Vault generates a dynamic secret, it returns a lease_id, which is the value a user can use to renew or revoke the lease. The HashiCorp Vault documentation states: 'When creating a dynamic secret, Vault always returns a lease_id. This lease_id can be used to do a vault lease renew or a vault lease revoke command to manage the lease of a secret.' The lease_id uniquely identifies the lease associated with the dynamic secret, enabling precise management of its lifecycle.

The documentation under the 'Lease Renew and Revoke' section explains: 'Every secret in Vault is associated with a lease. When that lease expires, Vault revokes the secret and removes access to it. Associated with every lease is a unique lease_id. This identifier can be used to renew the lease before it expires or revoke it manually.' In contrast, renewable is a boolean indicating if the lease can be renewed, not a value for management. token_ttl relates to token duration, not lease management. lease_max is not a standard term in Vault's lease system. Thus, D (lease_id) is the correct answer.


HashiCorp Vault Documentation - Leases: Lease Renew and Revoke

Question 13

The Vault encryption key is stored in Vault's backend storage.

Correct Answer: B. False
Explanation:

The statement is false. The Vault encryption key is not stored in Vault's backend storage, but rather in Vault's memory. The Vault encryption key is the key that is used to encrypt and decrypt the data that is stored in Vault's backend storage, such as secrets, tokens, policies, etc. The Vault encryption key is derived from the master key, which is generated when Vault is initialized. The master key is split into unseal keys using Shamir's secret sharing algorithm, and the unseal keys are distributed to trusted operators. To start Vault, a quorum of unseal keys is required to reconstruct the master key and derive the encryption key. The encryption key is then kept in memory and used to protect the data in Vault's backend storage. The encryption key is never written to disk or exposed via the API. Reference: Seal/Unseal | Vault | HashiCorp Developer, Key Rotation | Vault | HashiCorp Developer


Question 14

You can build a high availability Vault cluster with any storage backend.

Correct Answer: B. False
Explanation:

Not all storage backends support high availability mode for Vault. Only the storage backends that support locking can enable Vault to run in a multi-server mode where one server is active and the others are standby. Some examples of storage backends that support high availability mode are Consul, Integrated Storage, and ZooKeeper. Some examples of storage backends that do not support high availability mode are Filesystem, MySQL, and PostgreSQL. Reference: https://developer.hashicorp.com/vault/docs/concepts/ha1, https://developer.hashicorp.com/vault/docs/configuration/storage2


Question 15

Which of the following statements are true about HCP Vault Dedicated? (Select three)

Correct Answer: B. Helps reduce operational overhead for organizations with push-button deployment and fully managed upgrades; C. Increases reliability and ease of use so you can onboard applications and teams easily; D. Increases security across clouds and machines through a single interface
Explanation:

Comprehensive and Detailed in Depth Explanatio n:

HCP Vault Dedicated is a managed cloud service offering specific benefits over self-managed Vault. The HashiCorp Vault documentation outlines its advantages: 'Vault Enterprise running on the HashiCorp Cloud Platform (HCP) enables users to secure, store, and tightly control access to tokens, passwords, certificates, and encryption keys within one unified cloud-based platform.' It lists the following benefits relevant to the options:

B (Helps reduce operational overhead for organizations with push-button deployment and fully managed upgrades): The documentation states, 'Reduce operational overhead: Push-button deployment, fully managed upgrades, and backups mean organizations can focus on adoption and integration instead of operational overhead.' This reflects HCP Vault Dedicated's managed nature, automating deployment and maintenance tasks.

C (Increases reliability and ease of use so you can onboard applications and teams easily): It notes, 'Ease of use: HCP Vault Dedicated is built around making cloud security automation simple. Get up and running quickly so that you can onboard applications and teams easily,' and 'Reliability: HashiCorp has experience supporting thousands of commercial Vault Enterprise clusters and HCP Vault Dedicated brings that expertise directly to users.' This simplifies onboarding and ensures dependable operation.

D (Increases security across clouds and machines through a single interface): The docs confirm, 'Increase security across clouds and machines: Secure your infrastructure across all your environments through a single interface and globally control and restrict access to sensitive data and systems,' highlighting centralized security management.

However, A (Provides 100% feature parity compared to Vault self-managed clusters) is false. The documentation clarifies under 'Feature Parity': 'HCP Vault Dedicated does not provide 100% feature parity compared to Vault self-managed clusters. While it offers many of the same features and capabilities, there may be some differences or limitations in functionality between the two deployment options.' Thus, B, C, and D are true.


HashiCorp Vault Documentation - What is HCP Vault: Feature Parity