
Limited-Time Offer: Enjoy 50% Savings! Ends in 00h 00m 00s Coupon code: 50OFF
Skip to content

Free IBM Certified Analyst - Security QRadar SIEM V7.5 C1000-162 Exam Questions

Page: 1 / 7 Total 64 questions

Want more questions? Get Premium Access.

Question 1

Events can be exported from the QRadar Log Activity tab in which file formats?

Correct Answer: D. XML and CSV
Explanation:

Events can be exported from the QRadar Log Activity tab in XML (Extensible Markup Language) or CSV (Comma-Separated Values) formats, providing flexibility in how data is extracted and used for further analysis outside of QRadar.
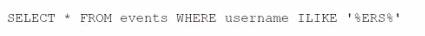

Question 2

How long does QRadar store payload indexes by default?

Correct Answer: B. 30 days
Explanation:

By default, QRadar stores payload indexes for a duration of 30 days. This retention period is configurable, allowing administrators to adjust how long specific data is retained based on their requirements.


Question 3

A task is set up to identify events that were missed by the Custom Rule Engine. Which two (2) types of events does an analyst look for?

Correct Answer: A. Log Only Events sent to a Data Store; D. High Level Category Unknown Events
Explanation:

To identify events that were missed by the Custom Rule Engine (CRE) in IBM Security QRadar SIEM, an analyst would primarily look for 'Log Only Events sent to a Data Store' and 'High Level Category Unknown Events.' Log Only Events are those that are stored directly without being processed by the CRE, indicating they might have been overlooked or not matched by any existing rules. High Level Category Unknown Events are those that do not fit into any of the predefined categories in QRadar, suggesting that the CRE might not have rules to handle or categorize these events properly. These types of events are crucial for analysts to review to ensure that no significant incidents are missed and to refine the rule set for better detection in the future.


Question 4

On the Reports tab in QRadar. what does the message "Queued (position in the queue)" indicate when generating a report?

Correct Answer: D. The report is queued for generation and the message indicates the position of the report in the queue.
Explanation:

In the Reports tab of QRadar, the message 'Queued (position in the queue)' indicates that the report is queued for generation. The message provides the position of the report within the generation queue, which helps users understand the report's status and expected generation time


Question 5

Which two (2) options are used to search offense data on the By Networks page?

Correct Answer: B. Events/Flows; E. Network
Explanation:

To search offense data on the By Networks page, an analyst can use the options 'Events/Flows' to filter based on the types of data points, and 'Network' to specify the network they want to search for. This allows for a focused search on specific networks and types of data.


Question 6

Which statement regarding saved event search criteria is true?

Correct Answer: B. Saved search criteria does not expire
Explanation:

In QRadar, when you save search criteria, especially on the Offenses tab, the configured search criteria are retained for future use and do not expire. This permanence ensures that users can quickly access and reuse their preferred search configurations, thereby streamlining the process of monitoring and investigating offenses over time.


Question 7

Which flow fields should be used to determine how long a session has been active on a network?

Correct Answer: C. Start time and last packet time

Question 8

Which two (2) components are necessary for generating a report using the QRadar Report wizard?

Correct Answer: A. Saved search; C. Layout
Explanation:

In IBM Security QRadar SIEM, generating a report using the QRadar Report Wizard requires a 'Saved Search' and a 'Layout.' A Saved Search is a predefined search criterion that users save in QRadar to reuse for various reporting or analysis purposes. It acts as the data source for the report, defining what data will be included. The Layout component refers to the structure and presentation of the report, including how the data from the Saved Search is organized and displayed. It encompasses the formatting, charts, tables, and other visual elements that make up the final report. Together, these components ensure that reports are not only informative but also well-organized and readable, catering to the specific informational needs and preferences of the users or stakeholders.


Question 9

What Is the result of the following AQL statement?

Correct Answer: B. Returns all fields where the username contains the ERS string and is case-insensitive
Explanation:

The AQL (Ariel Query Language) statement provided would return all fields from the 'events' table where the 'username' column contains the string 'ERS', regardless of case. The 'ILIKE' operator in AQL is used for case-insensitive pattern matching, which means that it will match 'ers', 'Ers', 'ErS', etc.


Question 10

What feature in QRadar uses existing asset profile data so administrators can define unknown server types and assign them to a server definition in building blocks and in the network hierarchy?

Correct Answer: C. Server discovery
Explanation:

In IBM Security QRadar SIEM V7.5, the feature that utilizes existing asset profile data to define unknown server types and assign them to server definitions in building blocks and in the network hierarchy is known as 'Server Discovery.' This feature grants permission to discover servers, thereby enabling administrators to identify and classify various server types within their network infrastructure, enhancing the overall asset management and security posture.