The Chief Compliance Officer plans to enhance privacy management in the working environment. You need to recommend a solution to enhance the privacy management. The solution must meet the following requirements:
* Identify unused personal data and empower users to make smart data handling decisions.
* Provide users with notifications and guidance when a user sends personal data in Microsoft Teams.
* Provide users with recommendations to mitigate privacy risks.
What should you include in the recommendation?
Correct Answer:C. Privacy Risk Management in Microsoft Priva
Explanation:
Privacy Risk Management in Microsoft Priva gives you the capability to set up policies that identify privacy risks in your Microsoft 365 environment and enable easy remediation. Privacy Risk Management policies are meant to be internal guides and can help you:
Detect overexposed personal data so that users can secure it.
Spot and limit transfers of personal data across departments or regional borders.
Help users identify and reduce the amount of unused personal data that you store.
You have an Azure subscription that contains virtual machines, storage accounts, and Azure SQL databases. All resources are backed up multiple times a day by using Azure Backup. You are developing a strategy to protect against ransomware attacks.
You need to recommend which controls must be enabled to ensure that Azure Backup can be used to restore the resources in the event of a successful ransomware attack.
Which two controls should you include in the recommendation? Each correct answer presents a complete solution. NOTE: Each correct selection is worth one point.
Correct Answer:A. Use Azure Monitor notifications when backup configurations change.; B. Require PINs for critical operations.
'You need to recommend which CONTROLS must be enabled to ENSURE that Azure Backup can be used to RESTORE the resources in the event of a successful ransomware attack.' Whilst helpful for auditing purposes and detection of a malicious attack, monitoring configuration changes and alerting after a change is made does not represent a CONTROL which ENSURES Azure Backup can be used to RESTORE the resources.
Question 5
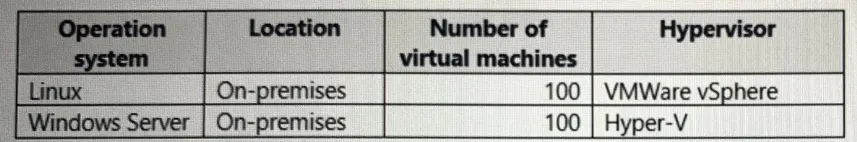
Your company has the virtual machine infrastructure shown in the following table.
The company plans to use Microsoft Azure Backup Server (MABS) to back up the virtual machines to Azure.
You need to provide recommendations to increase the resiliency of the backup strategy to mitigate attacks such as ransomware.
What should you include in the recommendation?
Correct Answer:C. Require PINs to disable backups.
You are designing the encryption standards for data at rest for an Azure resource
You need to provide recommendations to ensure that the data at rest is encrypted by using AES-256 keys. The solution must support rotating the encryption keys monthly.
Solution: For blob containers in Azure Storage, you recommend encryption that uses Microsoft-managed keys within an encryption scope.
You have a Microsoft 365 subscription that contains a group named Group1. The subscription contains 1,000 Windows devices that are joined to a Microsoft Entra tenant and managed by using Microsoft Intune. All users sign in to the devices by using standard user accounts.
You plan to deploy a new app named App1 to the members of Group1. The Group1 members must have administrative rights to install new versions of App1.
You need to ensure that the Group1 members can install new versions of App1. The solution must follow the principles of Zero Trust.
You have an Azure subscription that contains multiple network security groups (NSGs), multiple virtual machines, and an Azure Bastion host named bastion1.
Several NSGs contain rules that allow direct RDP access to the virtual machines by bypassing bastion!
You need to ensure that the virtual machines can be accessed only by using bastion! The solution must prevent the use of NSG rules to bypass bastion1.
To ensure virtual machines can only be accessed through Azure Bastion and prevent NSG rule bypass:
Azure Bastion Standard tier: The Standard tier of Azure Bastion provides enhanced security features including the ability to enforce Bastion-only access and restrict direct RDP connections.
Native client support: Enables secure access while preventing RDP port (3389) exposure directly from NSGs. This feature allows only Bastion to access VMs regardless of NSG rules.
NSG remediation: Configure NSGs to deny direct RDP access (port 3389) from all sources except Azure Bastion's internal subnet. Bastion communicates with VMs over private channels that bypass traditional NSG RDP rules.
Enforcement mechanism: Bastion Standard provides built-in enforcement that any VM connected to Bastion cannot be accessed except through Bastion, preventing NSG rules from circumventing this control.
Alternative approach: Ensure NSG rules are configured to deny port 3389 from all external sources and allow only Bastion's subnet. However, Standard tier enforcement is the robust solution.
Deploy Azure Bastion in Standard tier with native client support and configure NSG rules to deny direct RDP access, ensuring all VM access routes through Bastion regardless of other NSG configurations.
Question 9
Your company has an Azure subscription that has enhanced security enabled for Microsoft Defender for Cloud.
The company signs a contract with the United States government.
You need to review the current subscription for NIST 800-53 compliance.
What should you do first?
Correct Answer:D. From Defender for Cloud, add a regulatory compliance standard.
Your company plans to deploy several Azure App Service web apps. The web apps will be deployed to the West Europe Azure region. The web apps will be accessed only by customers in Europe and the United States.
You need to recommend a solution to prevent malicious bots from scanning the web apps for vulnerabilities. The solution must minimize the attach surface.
What should you include in the recommendation?
Correct Answer:D. Azure Traffic Manager and application security groups
The company plans to hire several temporary employees within a brief period. The temporary employees will need to access applications and data on the company' premises network.
The company's security policy prevents the use of personal devices for accessing company data and applications.
You need to recommend a solution to provide the temporary employee with access to company resources. The solution must be able to scale on demand.
What should you include in the recommendation?
Correct Answer:D. Deploy Azure Virtual Desktop, Azure Active Directory (Azure AD) Conditional Access, and Microsoft Defender for Cloud Apps.
You have an Azure AD tenant that syncs with an Active Directory Domain Services (AD DS) domain.
You have an on-premises datacenter that contains 100 servers. The servers run Windows Server and are backed up by using Microsoft Azure Backup Server (MABS).
You are designing a recovery solution for ransomware attacks. The solution follows Microsoft Security Best Practices.
You need to ensure that a compromised administrator account cannot be used to delete the backups
What should you do?
Correct Answer:A. From a Recovery Services vault generate a security PIN for critical operations.
Explanation:
To ensure a compromised administrator account cannot delete backups, you should: Implement Azure Backup immutability features through retention lock settings that prevent deletion or modification of backup data, even by administrators with full permissions. Additionally: (1) Use Azure Role-Based Access Control (RBAC) to restrict backup deletion permissions to a separate administrative role, (2) Configure backup data to be stored in a separate subscription or resource group with restricted access, and (3) Enable Multi-User Authorization (MUA) in MABS to require approval from multiple administrators for critical backup operations. The immutability setting is the primary technical control that prevents ransomware operators from destroying recovery options.
Question 15
You have an Azure subscription that has Microsoft Defender for Cloud enabled. You need to enforce ISO 2700V2013 standards for the subscription. The solution must ensure that noncompliant resources are remediated automatically