Limited-Time Offer: Enjoy 50% Savings! Ends in 00h 00m 00s Coupon code: 50OFF
Skip to content

Free Palo Alto Networks XSIAM Engineer XSIAM-Engineer Exam Questions

Page: 1 / 6 Total 59 questions

Want more questions? Get Premium Access.

Question 1

A Cortex XSIAM engineer adds a disable injection and prevention rule for a specific running process. After an hour, the engineer disables the rule to reinstate the security capabilities, but the capabilities are not applied.

What is the explanation for this behavior?

Correct Answer: A. The engineer needs to restart the process to get back the security capabilities.
Explanation:

When a disable injection and prevention rule is applied to a running process, the security capabilities are detached for the lifetime of that process. Even after disabling the rule, the capabilities are not reapplied automatically; the process must be restarted to restore security enforcement.

Question 2

A CISO has asked an engineer to create a custom dashboard in Cortex XSIAM that can be filtered to show incidents assigned to a specific user.

Which feature should be used to filter the incident data in the dashboard?

Correct Answer: A. Filters and inputs in the custom dashboard
Explanation:

To show incidents assigned to a specific user in a Cortex XSIAM custom dashboard, the engineer should use filters and inputs in the custom dashboard. This enables dynamic filtering of incident data, allowing the dashboard to be customized based on user assignment.


Question 3

What is the function of the "MODEL" section when creating a data model rule?

Correct Answer: D. To map log fields to corresponding Cortex XSIAM Data Model (XDM) fields
Explanation:

The MODEL section in a data model rule is used to map log fields to the corresponding Cortex XSIAM Data Model (XDM) fields. This ensures that ingested data aligns with XDM, enabling consistent analytics, detections, and queries across different data sources.


Question 4

When activating the Cortex XSIAM tenant, how is the data at rest configured with AES 128 encryption?

Correct Answer: B. Under Advanced, choose 'BYOK,' and adhere to the wizard's instructions as outlined in the encryption method section.
Explanation:

During Cortex XSIAM tenant activation, data at rest is configured with AES 128 encryption by selecting 'BYOK' (Bring Your Own Key) under the Advanced Encryption Method option and following the wizard's instructions. This ensures secure key management and compliance with encryption standards.


Question 5

Which action will prevent the automatic extraction of indicators such as IP addresses and URLs from a script's output?

Correct Answer: C. Use 'AutoExtract': False in the script.
Explanation:

To prevent Cortex XSIAM from automatically extracting indicators (like IPs, domains, and URLs) from a script's output, you must use 'AutoExtract': False in the script. This disables the auto-extraction mechanism for that script.


Question 6

Which action is required to enable use of a custom script in an alert layout?

Correct Answer: D. Tag the script with 'general-purpose-dynamic-section.' add a general purpose dynamic section, and edit the section settings to add the automation script.
Explanation:

To use a custom script in an alert layout, the script must be tagged with 'general-purpose-dynamic-section', then a general purpose dynamic section is added to the layout, and finally the section settings are edited to attach the automation script. This ensures the script executes and displays results dynamically within the alert layout.


Question 7

A security engineer notices that in the past week ingestion has spiked significantly. Upon investigating the anomaly, it is determined that a custom application developed in-house caused the spike. The custom application is sending syslog to the Broker VM Syslog Collector applet. The engineer consults with the SOC analyst, who determines that 90% of the logs from the custom application are not used.

What can the engineer configure to reduce the ingestion?

Correct Answer: A. Parsing rule to drop the unnecessary data at the Broker VM
Explanation:

To reduce ingestion from the custom application, the engineer should configure a parsing rule on the Broker VM. Parsing rules can be set to drop unnecessary data before it is ingested into Cortex XSIAM, preventing wasteful log volume and optimizing system efficiency.


Question 8

Which installer type should be used when upgrading a non-Linux Kubernetes cluster?

Correct Answer: B. Helm
Explanation:

For upgrading a non-Linux Kubernetes cluster, the correct installer type is Helm, since Helm charts are the supported method for deploying and managing Cortex XDR agents in Kubernetes environments.


Question 9

In the Incident War Room, which command is used to update incident fields identified in the incident layout?

Correct Answer: A. !setIncidentFields
Explanation:

The !setIncidentFields command is used in the Incident War Room to directly update incident fields that are defined in the incident layout, ensuring the incident record reflects the latest information.


Question 10

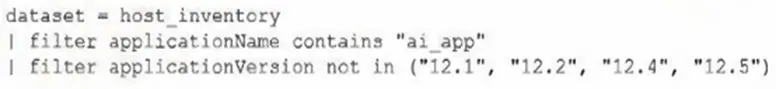
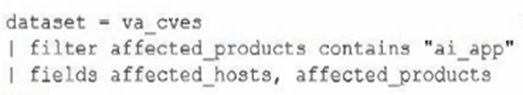
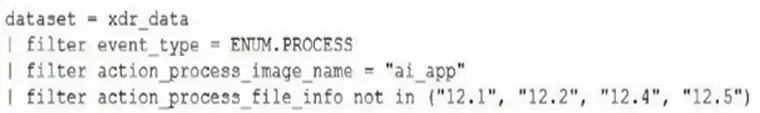
A vulnerability analyst asks a Cortex XSIAM engineer to identify assets vulnerable to newly reported zero-day CVE affecting the "ai_app" application and versions 12.1, 12.2, 12.4, and 12.5.

Which XQL query will provide the required result?

A)

B)

C)

D)

Correct Answer: C. Option C
Explanation:

The correct query is the preset = host_inventory_applications with filters for application_name contains 'ai_app' and version in ('12.1', '12.2', '12.4', '12.5'). This directly identifies hosts that have the vulnerable application and specific versions installed, matching the analyst's request to find assets exposed to the zero-day CVE.