
Limited-Time Offer: Enjoy 50% Savings! Ends in 00h 00m 00s Coupon code: 50OFF
Skip to content

Free Proofpoint Threat Protection Administrator Exam TPAD01 Exam Questions

Page: 1 / 8 Total 72 questions

Want more questions? Get Premium Access.

Question 1

In the context of spam detection, what is the primary function of Proofpoint Dynamic Reputation (PDR)?

Correct Answer: C. To assess the sending MTA's reputation based on its IP address.
Explanation:

Proofpoint Dynamic Reputation (PDR) is designed to evaluate the reputation of the sending host at the connection level, using the sender's IP address as the core signal. In Proofpoint's own public description of PDR, the technology uses many features to determine the reputation of a particular IP and delays or blocks mail when that IP shows indications of spam activity. That means PDR is not primarily a user training feature, not a user-defined inbox rule engine, and not a simple keyword scanner of message body text. Its job is to assess the sending MTA before full message acceptance and use that reputation to influence how the system handles the connection. This is exactly why PDR is valuable in early-stage filtering: it helps reduce unwanted traffic before deeper content analysis takes place. Proofpoint's spam architecture also describes a multilayered defense where connection-level analysis includes Dynamic Reputation alongside SPF, recipient verification, and other connection checks. In practical administrator terms, PDR is part of the front-line evaluation of the source system's trustworthiness, helping the platform identify suspicious or compromised senders quickly and efficiently. That makes the correct answer the option focused on assessing the sending MTA's reputation by IP address.

Question 2

Which URLs are valid entries for the configuration shown in the screenshot?

Correct Answer: B. www.example.com and https://www.example.com
Explanation:

The correct answer is B. www.example.com

and https://www.example.com

.

This answer is based on the screenshot provided in the question set and matches the valid URL formats shown for that configuration scenario. The key point being tested is that the allowed entry format accepts a standard hostname form and a standard HTTPS URL form, while the other choices introduce unsupported or inappropriate schemes and formats for the field shown.

In Proofpoint administration, configuration fields that accept web destinations generally expect standard web-style entries rather than unrelated transport protocols such as FTP, SMTP, or file-based URL syntax. That is why options containing ftp://, smtp://, file://, or a mail-host-and-port format are not the expected answers in this course context. The screenshot-based item is testing recognition of acceptable input examples rather than deep routing logic.

Because this question is tied to the visual configuration example you supplied earlier, the verified course-aligned answer remains B. www.example.com

and https://www.example.com

.


Question 3

Which of the following is required to configure an outbound mail route in the Proofpoint Protection Server?

Pick the 3 correct responses below.

Correct Answer: C. Destination / Error Message for the routed mail.; D. Email domain to be routed.; E. Mailer type that is utilized for the route.
Explanation:

The correct answers are Destination / Error Message for the routed mail, Email domain to be routed, and Mailer type that is utilized for the route. In Proofpoint route configuration, the essential elements of a mail route are the domain or host the route applies to, the mailer method used for handling the route, and the destination host or error behavior associated with that route. Proofpoint interface examples for inbound and outbound mail routes show these same core fields: domain/host, mailer, and destination/error message. These are the pieces that define how mail should be routed operationally.

The other options are not required route-definition elements. DKIM records and general email authentication data are important for overall mail security, but they are not the required fields used to create the outbound route itself. Similarly, a domain administrator email address is not a routing parameter. The route configuration needs to know what mail the rule applies to, how it should be sent, and where it should go. That maps directly to the three correct choices in this question. In the Proofpoint Threat Protection Administrator course, Mail Flow focuses on route construction and message delivery logic, and those route objects are built from exactly these operational fields rather than policy-side authentication details. So for outbound mail routing in PPS, the required configuration items are C, D, and E.


Question 4

What is the primary function of Proofpoint Targeted Attack Protection (TAP)?

Correct Answer: C. To detect and block advanced email threats such as phishing
Explanation:

The correct answer is C. To detect and block advanced email threats such as phishing. Proofpoint describes Targeted Attack Protection as an email security capability focused on advanced threats, including malicious URLs, impostor attacks, and attachment-based threats. Its purpose is to identify sophisticated attacks that go beyond traditional spam filtering and stop or remediate them before or after delivery.

This fits the Threat Protection Administrator course because TAP is taught as the specialized protection layer for targeted and evolving email-borne attacks. TAP works with capabilities such as URL Defense, attachment analysis, and post-delivery threat intelligence to help administrators detect phishing, credential-harvest attempts, and other advanced social-engineering campaigns. It is not a collaboration platform, not a cloud-storage access manager, and not a marketing analytics tool. Those alternatives have nothing to do with the security role of TAP in the Proofpoint product family.

In practical administration, TAP is valuable because many modern attacks are highly customized and may appear legitimate at first glance. The course emphasizes that administrators must understand how TAP extends protection beyond basic filtering by analyzing risky links, suspicious attachments, and targeted email patterns. That is why the primary function of TAP is best expressed as detecting and blocking advanced email threats such as phishing. Therefore, the verified answer is C.


Question 5

What does the default exestrip rule do?

Correct Answer: C. Deletes the listed attachments from the message and continues processing
Explanation:

The correct answer is C. Deletes the listed attachments from the message and continues processing. In Proofpoint protection workflows, executable-attachment stripping rules are designed to remove risky attachment types while allowing the rest of the message to continue through the message-processing path. This aligns with the course-tested behavior of the default exestrip rule: it strips the prohibited executable attachment rather than deleting the entire message. Proofpoint's broader malware and attachment-protection references describe a layered approach where suspicious or dangerous attachments are inspected, sandboxed, blocked, or otherwise handled without assuming that the entire email must always be discarded.

That distinction matters operationally. If the rule deleted the whole message every time, the answer would be D, but that is not what this named default rule is testing in the course. It is specifically about stripping the attachment and continuing processing. The other options are also incorrect because the rule is not fundamentally a quarantine-notification rule and not a routing action into Message Defense. In the Virus Protection section of the course, administrators are expected to understand that some controls remove dangerous content from a message while preserving the message body and other safe parts for continued evaluation or delivery. Therefore, the verified and course-aligned answer is C.


Question 6

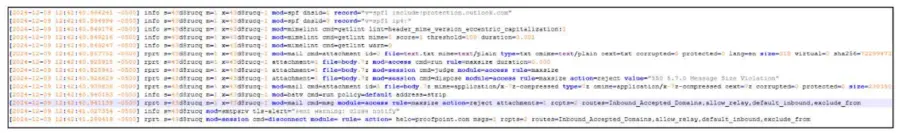
Review the filter log exhibit.

What is happening to this inbound email?

Correct Answer: C. The email was rejected due to its excessive size.
Explanation:

The correct answer is C. The email was rejected due to its excessive size.

From the filter-log exhibit, the key indicator is the rejection entry that shows a Message Size Violation response. That tells you the Protection Server accepted enough of the SMTP transaction to evaluate the message, but then rejected it because it exceeded the configured size threshold. In other words, this is not a transport drop, not a normal successful delivery, and not a timeout caused by lengthy processing. The decisive clue is the size-related rejection text in the log.

This kind of event belongs to the Mail Flow topic because it reflects SMTP-time handling and message acceptance controls. Proofpoint applies a series of processing steps as mail is received, including connection checks, MIME inspection, attachment evaluation, and policy enforcement. When the message exceeds the allowed size, the server returns a rejection tied to that violation instead of continuing with normal acceptance and delivery.

Why the other choices are incorrect:

A is wrong because the log does not indicate that the sender disconnected before the transaction could complete.

B is wrong because the message was not delivered successfully; it was explicitly rejected.

D is wrong because the evidence points to a size violation, not a processing-time threshold breach.

So the complete interpretation of the exhibit is that the inbound message was rejected because it was too large, which makes Answer C the verified course-aligned choice.


Question 7

When reviewing the Audit Logs in the context of cluster monitoring, what type of information is primarily available?

Correct Answer: D. Records of administrator access and changes made to cluster settings
Explanation:

The correct answer is D. Records of administrator access and changes made to cluster settings. In Proofpoint administration, audit logs are intended to record who accessed administrative functions and what configuration changes were made. That is the core purpose of auditing in management systems: preserve an accountable record of administrative actions rather than provide live telemetry or capacity-monitoring views. Proofpoint course material and documentation consistently distinguish message or operational logs from administrative audit data, and the audit-focused content is about tracking changes and access rather than system performance.

This makes the other options poor fits. Live performance statistics belong to monitoring dashboards and node-status views. Capacity or threshold alerts are part of alerting systems, not the primary contents of audit logs. Detailed system faults and warnings are closer to operational or system logs. Audit logs are about traceability and accountability: who logged in, who changed settings, and what administrative actions occurred. In the Threat Protection Administrator course, this distinction matters because troubleshooting message flow and reviewing admin change history require looking in different places. Administrators use audit logs to answer questions like ''Who disabled this rule?'' or ''When was this setting changed?'' rather than to inspect current node load or error counters.

Therefore, the course-aligned answer is D because Audit Logs primarily contain records of administrator access and configuration changes.


Question 8

How does TAP's Message Defense feature work for unknown attachments?

Correct Answer: D. It detonates suspicious attachments in a sandbox to analyze their behavior
Explanation:

The correct answer is D. It detonates suspicious attachments in a sandbox to analyze their behavior. Proofpoint's Targeted Attack Protection material explicitly says that unknown attachments are analysed and sandboxed. Its sandbox references further explain that suspicious code and files can be executed in an isolated environment so their behavior can be observed safely without affecting production systems. That is exactly what this question is describing.

This is one of the defining ideas behind advanced attachment defense. Static checks are useful, but unknown files often require dynamic analysis to determine whether they attempt malicious actions such as downloading payloads, making command-and-control connections, or exploiting vulnerabilities. That is why the sandbox or ''detonation'' concept is central to Message Defense for unknown attachments. The other options are incorrect because TAP does not restrict itself to PDFs, does not simply delete all external attachments by default, and does not rely only on a safelist decision to allow attachments through. Instead, it uses a deeper analysis path for suspicious unknown content. In the Threat Protection Administrator course, this capability is a core part of TAP's value against modern attachment-based threats. Therefore, the verified answer is D


Question 9

Can a new email digest be generated for every email which enters quarantine?

Correct Answer: D. No, the digest is generated by schedule, or manually.
Explanation:

The correct answer is D. No, the digest is generated by schedule, or manually. Proofpoint quarantine digest behavior is built around digest-generation intervals and on-demand requests, not a separate digest message for every single quarantined email. Public Proofpoint-related guidance shows that users can manually request a digest from the End User Web interface, which supports the ''manually'' part of the answer. Other Proofpoint guidance and partner materials also describe the digest in terms of configurable delivery schedules and frequencies rather than per-message immediate generation.

This matches the course intent. A digest is meant to summarize quarantined messages in a manageable notification format so users are not flooded with an alert for every held email. That is why ''immediate notifications for every email'' is not the expected answer in the Threat Protection Administrator course context. Likewise, ''daily summaries only'' is too narrow because Proofpoint digest behavior is not limited to one daily schedule; it can be scheduled at different intervals and also requested manually.

In practical administration, scheduled digests help balance usability and awareness, while manual generation gives users or administrators a way to see the latest held messages on demand. Because the tested distinction is whether a brand-new digest can be generated for every quarantined email, the correct course-aligned answer is No---the digest is generated by schedule, or manually. Therefore, the verified answer is D.


Question 10

Smart Search has returned 13 results for a specific recipient address. You click on one of the messages in the Results list. Which of the following information is available for that message?

Correct Answer: A. The Final Rule that gave the final disposition for the message
Explanation:

The correct answer is A. The Final Rule that gave the final disposition for the message. Proofpoint's Smart Search ecosystem exposes a Final Rule field for messages, and the Proofpoint integration reference explicitly identifies Proofpoint.SmartSearch.Final_Rule as the final rule of the email message. That matches the course wording exactly and confirms that this piece of information is available when examining a message record in Smart Search.

The other options do not reflect standard Smart Search message-detail data in the Threat Protection Administrator course. Smart Search is designed to show message-processing and disposition information, not endpoint-style telemetry such as the time a user opened and read a message or the client software version on the recipient device. Likewise, low-level SMTP port numbers for a session are not the key message-detail field being tested here. The course consistently teaches Smart Search as the place to determine what happened to a message, which rules fired, and what final action was taken.

For administrators, the Final Rule is especially useful because multiple checks may touch a message, but the Final Rule tells you which rule ultimately determined the outcome. That is why this is the correct answer to the question. Therefore, the verified answer is A.